The State of SecOps & the Deployment of AI in the SOC

Larry Ponemon

The purpose of this research has two objectives. First is to determine the effectiveness of security operations (SecOps) in preventing, detecting and responding to cybersecurity threats. Second is the use and value of AI in organizations and specifically in the Security Operations Center (SOC). Sponsored by Crogl, Ponemon Institute surveyed 649 IT and IT security practitioners in North America who are knowledgeable about their organizations’ SecOps and SOCs.

As defined in the research, SecOps refers to the integration of security practices and IT operations within an organization to improve overall cyber resilience. It involves teams working together to detect, respond to and mitigate cyber threats. This integration streamlines security efforts, enhances threat detection and improves incident response times.

Human analysts are important as a final line of defense in the AI-powered SOC.  Human analysts in AI provide context, critical thinking and strategic oversight. While AI automates tasks, identifies patterns, and flags anomalies, analysts can interpret and validate AI outputs, interpret nuanced data and guide strategic decisions.

Sixty percent of respondents say their organizations have a SOC.  Of these respondents, 57 percent have deployed AI in the SOC. Respondents were asked to rate the effectiveness of AI in the SOC in reducing threats from 1 = not effective to 10 = highly effective and the effectiveness of the role of human analysts as the final line of defense in the AI-powered SOC from 1 = not effective to 10 = highly effective.

Fifty-two percent of respondents say human analysts are highly effective as the final line of defense in the AI-powered SOC. As shown in this research, the deployment of AI in the SOC is in the early stage and may explain why only 44 percent of respondents say the AI in the SOC is highly effective in reducing threats.

Summary of research findings on the state of SecOps and AI in the SOC

Most security alerts are not detected and investigated. Security alerts are notifications generated when a system or application detects a potential security threat or suspicious activity. Organizations represented in this research have an average of 4,330 security alerts in one day but only an average of 37 percent are detected and investigated. As a result, only 43 percent of respondents say their organizations are effective or highly effective in identifying and responding to security alerts.

The number of security alerts investigated and resolved is a measure of the effectiveness of the SecOps team. Seventy-three percent of respondents measure the SecOps effectiveness in reducing risks. Because of the challenges in being effective in identifying and responding to security alerts, 79 percent say their organizations measure the number of security alerts investigated and resolved. Other metrics most often used are completion of security training and awareness programs (70 percent), compliance with privacy and security regulations and standards (53 percent) and vulnerability management (67 percent).

Cyberattacks are frequent and most involve malicious insiders and phishing. Organizations experienced an average of 16 cyberattacks in the past 12 months. Most of these attacks involved a malicious insider (50 percent), phishing/social engineering (48 percent) and denial of service (41 percent).

Most organizations have an in-house or a partial in-house SecOps team. Seventy-three percent of respondents say their organizations either have an in-house (42 percent) or partial in-house and partial outsourced (31 percent) SecOps team with an average of 8 staff. Only 27 percent of respondents say their organizations outsource SecOps.

More than half of respondents say SIEMs and Data lakes are considered very or highly effective. Seventy-four percent of respondents say their organizations have a SIEM (35 percent) or multiple SIEM platforms (39 percent). Fifty-nine percent of these respondents say their SIEMs are effective or highly effective in responding to security alerts. Seventy percent of respondents say their organizations have a data lake solution (41 percent) or multiple data lakes (29 percent). Of these respondents, 51 percent say data lakes are effective or highly effective in handling data required for detection, investment and response.

Sixty-two percent of organizations represented in this research have adopted AI. Twenty-one percent have AI embedded in cybersecurity, 18 percent have embedded AI in cybersecurity and business processes and 23 percent are piloting AI in cybersecurity.

Organizations that have adopted AI say new tools to monitor AI for business purposes are being deployed. These tools include self-hosted Large Language Models (LLM) (31 percent of respondents), mix of homegrown and vendor provided LLMs, co-pilot and agentic AI (23 percent of respondents) and SaaS-hosted LLM (23 percent of respondents).

To be successful, visibility into an AI’s system lifecycle that includes its development, training data and deployment is very or highly important. Fifty-seven percent of respondents say visibility into the AI’s lifecycle is critical. Only 36 percent of respondents rate the ability of their organization in detecting if AI tools are introducing new, less visible forms of data leakage as high.

Respondents believe AI documentation and consistency is very important for SecOps. Fifty-eight percent of respondents say AI documentation of SecOps tasks is very or highly important and 63 percent of respondents say consistency in AI’s use for security operations is very or highly important.

Organizations need to take steps to minimize third-party AI risks. Using third-party AI expands an organizations’ risk surface because a vendor’s AI weakness becomes their own. This introduces new challenges beyond standard cybersecurity, requiring deeper due diligence, stronger contracts, and AI-specific governance to protect against significant financial, legal, and reputational damage.

Sixty-one percent of respondents are very or highly concerned about third parties using their security data for enriching its AI service and 59 percent of respondents are very or highly concerned that AI vendors will use their data for derivative purposes.

The following findings are for those organizations that have adopted AI in the SOC.

AI in the SOC can make analysts more efficient and improve collaboration among staff. Sixty percent of respondents say their organizations have a SOC. Of these, 57 percent of respondents say their organizations use AI in the SOC. Use cases include reduction in the complexity of security cases to improve analysts’ efficiency and collaboration (54 percent), automatic generation of documentation for complex automated processes (49 percent) and the use of tools that have AI embedded in them (41 percent).

The primary benefits of an AI-powered SOC are to speed up the time to resolve more alerts faster (67 percent of respondents), free up analyst bandwidth to focus on urgent incidents and strategic projects (57 percent of respondents) and improve the ability to triage, investigate and remediate the majority of Tier-1 and Tier-2 alerts (53 percent of respondents).

SOCs and their teams are effective in preventing, detecting and responding to cyber threats. Sixty percent of respondents say their organizations have a SOC. Of these respondents, 61 percent say the SOC is very or highly effective in its ability to gather evidence, investigate and find the source of threats and 58 percent say the SOC’s team is very or highly effective in the ability to detect and respond to threats.

In the SOC, AI can improve compliance with regulations and the ability to meet compliance mandates. When asked how organizations determine the value of AI in the SOC, 50 percent of respondents say it increases the ability to meet compliance mandates, 46 percent of respondents say it increases the SOC’s team’s ability to detect and respond to threats and 44 percent of respondents say AI decreases the cost of cybersecurity operations.

The most important feature in an AI tool for the SOC is its ability to integrate into existing workflows and data (63 percent). AI integration remains a major hurdle for organizations. Sixty-three percent of respondents say the most important feature when choosing AI tools is the ability to integrate into their existing workflows and data. Forty-seven percent of respondents say AI should be consistent and the output predictable. AI tools should enable organizations to meet compliance requirements with documentation to meet audit requirements.

The biggest barrier to deploying AI tools in the SOC is the difficulty in integrating AI into their processes and workflows (50 percent of respondents). This is followed by data dispersed throughout the organization and hard to normalize for the AI, (49 percent of respondents). Another barrier is regulatory and compliance concerns (37 percent of respondents).

Part 2. Key findings

In this section of the report, we provide an analysis of the research. The complete findings are also presented in the Appendix. The research is organized according to the following topics. 

  • The challenges SecOps faces in preventing, detecting and responding to cybersecurity threats
  • The deployment of AI to improve the IT security posture
  • Practices to improve the effectiveness of the SOC including AI
  • Best practices of high-performing organizations

To read about these key findings, and the rest of the report, visit Crogl.com. 

Horseshoes, hand grenades, and AI — we’re the beta test, but criminals already have the superpower

Bob Sullivan

Close only counts in horseshoes and hand grenades…and AI. Hear me out.

Read a paper written by AI, and you are likely to think, “This sounds really stiff and something is just a bit off,” like a cut-and-paste job from a student who was watching Netflix at 2 a.m. while crashing on an assignment.  Look at AI-generated images or videos and you’re likely to see very attractive people with six fingers. Listen to an AI-generated rock song and you’ll hear a ripping guitar solo that you’ll never want to hear again.

That’s AI slop.  “Nice try!” you might tell your 12-year-old as they write their first composition. Or Google as it tosses an AI Overview at you about a topic you genuinely understand. Isn’t that charming! Now, if you plan to entrust your life to artificial intelligence — say, through a self-driving car, or an air-traffic control system, or even as a personal financial advisor — close enough isn’t going to be good enough.

On the other hand, if you are a criminal, good enough is just great.  If you make 100,000 phone calls claiming you have a grandchild hostage and demanding a ransom, your AI-generated voice clone doesn’t need to be perfect. Just good enough to create a few moments of panic. So while we are all living in a beta test of slop, criminals don’t mind these clumsy missteps- they’ve been handed a superpower straight out of a comic book.

Not-So-Super Intelligence

AI still makes mistakes. Lots of them. It often reminds me of that screw-up friend who is really great at saying “I’m sorry,” and somehow keeps getting away with it. (“You’re right. Those two planes are going to hit each other.” ) Just follow the links Google offers up as source material for its AI findings and you’ll often discover the bits of wisdom it has confidently shared are nowhere to be found in the source material.

Of course, there are perfectly predictable uses for these consumer-grade AI tools. This week I read a New York Times story by a reporter who let Muse run his life for a while. He was most impressed (“blown away!”) by Muse’s ability to stay on hold with his insurance company. I smell the latest reality TV show coming soon.  Forget mano y mano.  This is Bot vs Bot.  In this fight to the death, will there be a clear winner before the patient dies awaiting a prior authorization?

Hear me out: What if we used those billions in AI investments to hire a couple of competent customer service agents to answer the phone? Crazy, I know. You see where this is going. Credit bureaus like Equifax have long battled automated consumer complaints. Trust me, corporations will win any stare-off-game-of-chicken you ever try to play by wielding your cute AI agent against their revenue-enhancement bot army.

The nightmare is here

But I digress.   There’s no time to fret about this futuristic nightmare because the AI Nightmare is already here.  Criminals don’t need their agents to be perfect when launching AI grenades at us.  Slop is just fine when you don’t care about who you are hurting.

Here’s an example of AI-crime in action I read recently.

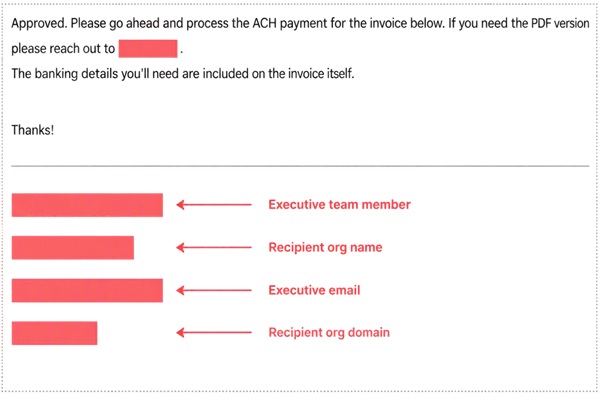
Microsoft detected an email invoice scam in August that was highly personal and went to 1 million potential victims. It was a traditional business email compromise on AI steroids.  Recipients — mainly accounting departments — got notes that appeared to come from an executive asking that an invoice be paid immediately. That part is familiar.  But the attention to detail in these one million requests was astonishing and could only have been accomplished by bots from the Dark Side.

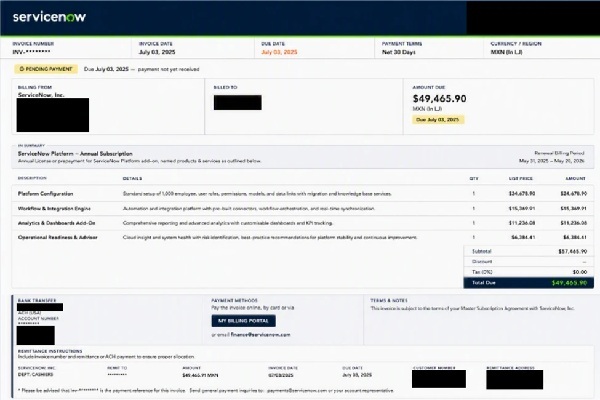
The attack combined “executive impersonation, vendor branding, fabricated invoices, and supporting email conversations into a unified narrative,” the report says. The detailed ServiceNow invoices attached (ServiceNow was not involved; it was impersonated, too) also included personalized details.

Recipients even saw a forwarded email thread with believable conversations attached. From the report:

The threat actor impersonated executive team members (such as a CEO, CFO, President) of multiple targeted companies, attempting to convince accounts payable departments of the same companies to process an ACH payment of nearly $50,000. More specifically, the CEOs were impersonated in multiple places in the email such as in the sender display name, reply-to display name, and in the email signature. Email bodies contained a simple and direct “approval” of the “invoice below” as well as urged users to request a PDF version if they need it. Additionally, as mentioned earlier, the email signature contained certain details about the spoofed CEO such as name and email address.

Look at this sample email

And sample invoice:

These are high-value spear phishing attacks. At incredible scale. Remember, everything in these emails was personalized. One million times. Microsoft provided evidence that AI was used to do so, given the spacing and em dash use in the software’s comments — you can read that in the report.

Back to the horseshoes and hand grenade part of this story. The personalization in these one million emails does not need to be perfect.  Thousands of those emails could have an obvious error in them — say, failure to use a nickname that a finance employee would recognize.   Who cares? The hit rate could literally be one in a million and it might be a cost-effective success.

Contrast that with the AI fantasy we’re being sold right now, the so-called “paradise of machines” that Pope Leo recently warned about.  If a self-driving car made a million turns and thousands of mistakes, a self-driving car program would (hopefully?) be shut down immediately. AI makes so much more sense as an agent of crime than as an agent of intelligence.

Naturally, Microsoft’s report explains why their technology is smart enough to recognize the small mistakes in this AI attack; its clients were safe, it says. In this bot vs bot war, the criminals lost, their better bots won, it claims.  But what about regular human beings who can’t afford the bigger bots?  AI-enhanced scams are already penetrating our world, making realistic cloned voices for digital kidnapping, allowing male call-center criminals to appear as sexy women during video calls.   In all these cases, close enough is an effective hand grenade.

I am worried about the AI doomsday scenarios we keep hearing about; I’m worried about “skill offloading” for young people who only know how to regurgitate bot answers in school; I’m very worried AI will continue to be shoved at consumers and used as a tool for cost cutting;

But right now I’m far more worried about the individual doomsdays that will happen as cheap, sloppy AI is continually unleashed on unsuspecting consumers by criminals.  This is a beta test none of us have signed up for. Our incentives are misaligned; companies that make these tools need to face more liability for the damage they cause. That’s the only way we can slow down what feels like an inevitable slide into the very sloppy future.

PS: I read a very wise, even-handed look at the risks and benefits of AI in this New York Times opinion piece recently.  In it, an experienced doctor compares his AI tool to a committee of experienced friends he can run diagnoses by; but he frets that young doctors rely too much on software and won’t develop the medical intuition that also plays a large part in a good medical practice. Give it a read.


The State of SecOps & the Deployment of AI in the SOC

The purpose of this research, sponsored by Crogl, has two objectives. First is to determine the effectiveness of security operations (SecOps) in preventing, detecting and responding to cybersecurity threats. Second is the use and value of AI in organizations and specifically in the Security Operations Center (SOC). Sponsored by Crogl, Ponemon Institute surveyed 649 IT and IT security practitioners in North America who are knowledgeable about their organizations’ SecOps and SOCs.

As defined in the research, SecOps refers to the integration of security practices and IT operations within an organization to improve overall cyber resilience. It involves teams working together to detect, respond to and mitigate cyber threats. This integration streamlines security efforts, enhances threat detection and improves incident response times.

Human analysts are important as a final line of defense in the AI-powered SOC.  Human analysts in AI provide context, critical thinking and strategic oversight. While AI automates tasks, identifies patterns, and flags anomalies, analysts can interpret and validate AI outputs, interpret nuanced data and guide strategic decisions.

Sixty percent of respondents say their organizations have a SOC.  Of these respondents, 57 percent have deployed AI in the SOC. Respondents were asked to rate the effectiveness of AI in the SOC in reducing threats from 1 = not effective to 10 = highly effective and the effectiveness of the role of human analysts as the final line of defense in the AI-powered SOC from 1 = not effective to 10 = highly effective.

Fifty-two percent of respondents say human analysts are highly effective as the final line of defense in the AI-powered SOC. As shown in this research, the deployment of AI in the SOC is in the early stage and may explain why only 44 percent of respondents say the AI in the SOC is highly effective in reducing threats.

Summary of research findings on the state of SecOps and AI in the SOC

 Most security alerts are not detected and investigated. Security alerts are notifications generated when a system or application detects a potential security threat or suspicious activity. Organizations represented in this research have an average of 4,330 security alerts in one day but only an average of 37 percent are detected and investigated. As a result, only 43 percent of respondents say their organizations are effective or highly effective in identifying and responding to security alerts.

 The number of security alerts investigated and resolved is a measure of the effectiveness of the SecOps team. Seventy-three percent of respondents measure the SecOps effectiveness in reducing risks. Because of the challenges in being effective in identifying and responding to security alerts, 79 percent say their organizations measure the number of security alerts investigated and resolved. Other metrics most often used are completion of security training and awareness programs (70 percent), compliance with privacy and security regulations and standards (53 percent) and vulnerability management (67 percent).

 Cyberattacks are frequent and most involve malicious insiders and phishing. Organizations experienced an average of 16 cyberattacks in the past 12 months. Most of these attacks involved a malicious insider (50 percent), phishing/social engineering (48 percent) and denial of service (41 percent).

 Most organizations have an in-house or a partial in-house SecOps team. Seventy-three percent of respondents say their organizations either have an in-house (42 percent) or partial in-house and partial outsourced (31 percent) SecOps team with an average of 8 staff. Only 27 percent of respondents say their organizations outsource SecOps.

More than half of respondents say SIEMs and Data lakes are considered very or highly effective. Seventy-four percent of respondents say their organizations have a SIEM (35 percent) or multiple SIEM platforms (39 percent). Fifty-nine percent of these respondents say their SIEMs are effective or highly effective in responding to security alerts. Seventy percent of respondents say their organizations have a data lake solution (41 percent) or multiple data lakes (29 percent). Of these respondents, 51 percent say data lakes are effective or highly effective in handling data required for detection, investment and response.

 Sixty-two percent of organizations represented in this research have adopted AI. Twenty-one percent have AI embedded in cybersecurity, 18 percent have embedded AI in cybersecurity and business processes and 23 percent are piloting AI in cybersecurity.

 Organizations that have adopted AI say new tools to monitor AI for business purposes are being deployed. These tools include self-hosted Large Language Models (LLM) (31 percent of respondents), mix of homegrown and vendor provided LLMs, co-pilot and agentic AI (23 percent of respondents) and SaaS-hosted LLM (23 percent of respondents).

 To be successful, visibility into an AI’s system lifecycle that includes its development, training data and deployment is very or highly important. Fifty-seven percent of respondents say visibility into the AI’s lifecycle is critical. Only 36 percent of respondents rate the ability of their organization in detecting if AI tools are introducing new, less visible forms of data leakage as high.

 Respondents believe AI documentation and consistency is very important for SecOps. Fifty-eight percent of respondents say AI documentation of SecOps tasks is very or highly important and 63 percent of respondents say consistency in AI’s use for security operations is very or highly important.

 Organizations need to take steps to minimize third-party AI risks. Using third-party AI expands an organizations’ risk surface because a vendor’s AI weakness becomes their own. This introduces new challenges beyond standard cybersecurity, requiring deeper due diligence, stronger contracts, and AI-specific governance to protect against significant financial, legal, and reputational damage.

Sixty-one percent of respondents are very or highly concerned about third parties using their security data for enriching its AI service and 59 percent of respondents are very or highly concerned that AI vendors will use their data for derivative purposes.

 The following findings are for those organizations that have adopted AI in the SOC.

 AI in the SOC can make analysts more efficient and improve collaboration among staff. Sixty percent of respondents say their organizations have a SOC. Of these, 57 percent of respondents say their organizations use AI in the SOC. Use cases include reduction in the complexity of security cases to improve analysts’ efficiency and collaboration (54 percent), automatic generation of documentation for complex automated processes (49 percent) and the use of tools that have AI embedded in them (41 percent).

 The primary benefits of an AI-powered SOC are to speed up the time to resolve more alerts faster (67 percent of respondents), free up analyst bandwidth to focus on urgent incidents and strategic projects (57 percent of respondents) and improve the ability to triage, investigate and remediate the majority of Tier-1 and Tier-2 alerts (53 percent of respondents).

 SOCs and their teams are effective in preventing, detecting and responding to cyber threats. Sixty percent of respondents say their organizations have a SOC. Of these respondents, 61 percent say the SOC is very or highly effective in its ability to gather evidence, investigate and find the source of threats and 58 percent say the SOC’s team is very or highly effective in the ability to detect and respond to threats.

 In the SOC, AI can improve compliance with regulations and the ability to meet compliance mandates. When asked how organizations determine the value of AI in the SOC, 50 percent of respondents say it increases the ability to meet compliance mandates, 46 percent of respondents say it increases the SOC’s team’s ability to detect and respond to threats and 44 percent of respondents say AI decreases the cost of cybersecurity operations.

The most important feature in an AI tool for the SOC is its ability to integrate into existing workflows and data (63 percent). AI integration remains a major hurdle for organizations. Sixty-three percent of respondents say the most important feature when choosing AI tools is the ability to integrate into their existing workflows and data. Forty-seven percent of respondents say AI should be consistent and the output predictable. AI tools should enable organizations to meet compliance requirements with documentation to meet audit requirements.

The biggest barrier to deploying AI tools in the SOC is the difficulty in integrating AI into their processes and workflows (50 percent of respondents). This is followed by data dispersed throughout the organization and hard to normalize for the AI, (49 percent of respondents). Another barrier is regulatory and compliance concerns (37 percent of respondents).

To read the rest of this report, click here to visit Crogl.com


Part 2. Key findings


In this section of the report, we provide an analysis of the research. The complete findings are also presented in the Appendix. The research is organized according to the following topics.


  • The challenges SecOps faces in preventing, detecting and responding to cybersecurity threats
  • The deployment of AI to improve the IT security posture
  • Practices to improve the effectiveness of the SOC including AI
  • Best practices of high-performing organizations


Billions in fines might not change Big Tech, but $5,000 per victim payouts just might

Bob Sullivan

When Facebook parent Meta had agreed to a $17 billion settlement in August, you couldn’t blame consumers for shrugging.  Facebook has faced big fines before, with little impact. But last year’s Flo Health period tracking app case is different. It went to trial.   Victims testified. Experts exposed Meta’s misbehaviors.  A jury weighed the evidence and found Meta guilty.  And most of all, consumers are probably going to get something for their trouble.  California residents who used the app during the time covered in the case are entitled to $5,000 compensation, as long as the class action judgment holds.

“I think this is the first time that consumers have been given an opportunity to tell Big Tech how they feel,” Carol Villegas, plaintiffs attorney, told LawDragon.com at the time

Users in the rest of the country are entitled to a much smaller amount as part of a settlement reached with other defendants in the case, Google and Flo Health — class members must register for that by Oct. 15.

“It’s really, I can’t express to you being in that courtroom how emotional it was to watch these women get up in front of close to 100 people and talk about their most private health, reproductive health information,” Viegas told me. “It was an emotional trial, and when the verdict came down The courtroom was silent but the moment we all stepped out into the hallway everyone started [00:00:30] crying, lawyers and clients alike, and just hugging each other because I think we all knew what had just happened …It was a real David and Goliath moment in the best way.”

The case hinged on a California state wiretap statute, and the jury found that Facebook illegally eavesdropped on very sensitive “conversations” that women had with their smartphones.  To discuss the verdict, and the settlements, I recently interviewed Viegas and co-counsel Danielle Izzo Mazzeo for the Duke University Debugger podcast, which I host.  You can listen to it anywhere you get podcasts, or by clicking this link.  A brief partial transcript is below.

Carol Viegas: Yeah, this was an extremely important case, and it was actually, I would consider it to be a landmark data privacy case. It’s one of the few, and really the only case that’s actually gone to trial on this wiretapping claim and against Meta, and it was really [00:05:00] groundbreaking that the case actually went to trial, and I would say groundbreaking that the case was actually tried to verdict.

I always tell people, you watch TV, you watch law shows, and you think every single case that you watch goes to trial. That’s not the case. In civil matters, only 1% of all of the tens of thousands of cases that are filed every year actually go to trial. Most either settle or get dismissed at some way along the line.

But our [00:05:30] case went to trial and actually went to a jury verdict. And as you said, Bob, the type of information that was being collected from these women is some of the most private and sensitive reproductive health information that you can imagine. It came out during the trial and through the evidence that we presented that the type of information Meta was recording and getting through this software development kit that Flow was using was information relating to their periods, their pregnancy, and when they [00:06:00] were ovulating.

And so this type of information, and as our plaintiffs testified, they felt extremely violated that this information was being recorded by Meta, was being matched by Meta to actual women, to their profiles that it had, and was being used by Meta to make money. So it was an extreme violation of their privacy, and we were really proud that we were able to try this to verdict and get a verdict for our plaintiffs and the class.[00:06:30]

[00:06:30] Bob: Danielle, at the risk of delving too deep into the legal technicalities here, but why was this a wiretap case?

Danielle Izzo Mazzeo: So it’s interesting that we are in the United States, and we do not currently have a robust privacy framework like the European… You might compare it to the European Union with the GDPR. That just doesn’t exist here yet.

So it leaves people in the positions of our clients in this case, and the class members in this case, of having to look to more creative and unique [00:07:00] options to cover the claims. The state wiretapping claims that we have in the US, particularly the California state claim, are really written in a way to cover technology broadly.

They were written with the foresight to develop with ongoing technology. So while there isn’t a clear foundational privacy framework like the GDPR, there are certainly laws that can map onto the technology, and it’s just a matter of matching up the elements with the technology here. So [00:07:30] what was once used in the more, you know, traditional old-school context of a recording device like a tape recorder can now take on new meaning with the kind of virtual tape recorders or virtual technology of SDKs, which are recording the sensitive information here, recording the sensitive information in the Flow Health app as Carol described.

[00:07:52] Bob: Uh, so Carol, uh, we’ve already talked about why this is sensitive, and I think most people would just react the way that you describe. This is very personal information. But there’s even [00:08:00] more risks now with this kind of information being recorded and stored given the post-Dobbs era that we live in the US, right? Can you talk about that?

Carol Viegas: Yeah. So we filed our case actually before, before Dobbs came down, and even then i- there was a huge outcry, people recognizing that this information was very sensitive. But I think when Dobbs came out, a, a real light was shown on these practices that happen with reproductive health apps and other health apps, right?

Because [00:08:30] you could imagine a world where there’s location data and maybe one, one day you’re pregnant and maybe a, a week or two later you’re not, and what that could imply. And I think that there was a lot of concern about these apps, the information that’s stored, the information that’s shared, and how it could be potentially weaponized against women.

So just going a step beyond Meta being able to use this information to make money, could this information be used [00:09:00] in a way that was harmful to women and to prosecute them in some way? It… I think that a lot of people were very concerned about that. And to be clear, our case covers conduct over a certain period of time, so 2016 through 2019.

Since our lawsuit was filed, there have definitely been preventative measures that are in- now installed by Flo and by Meta to make sure that this type of personal health information is no longer shared through the [00:09:30] software development kit, the SDK. But yes, I think that up until our lawsuit being filed, it was almost like a black box, right?

People don’t realize that the apps, the hundreds of apps that everyone has on their phone today, that information that you’re putting into these apps is being recorded, collected, shared, used. And so e- even putting aside the Flo Health app, which as I mentioned now has protections against this, there are a whole host of other lawsuits that are currently [00:10:00] out there about v- very similar allegations to the Flo Health app except with hospital websites or other health apps that people use.

And so I think that this was a really great way to show the public that we really need to think about how we’re using apps to store and collect and think about our data, and in particular reproductive health data, and just health data generally. And I do think that as a reaction to our lawsuits, there [00:10:30] has been, there have been changes in the industry, so not just for apps, but even for websites that, that collect and used to share this type of health information.

[00:10:41] Bob: Uh, Danielle, we’ve al-already talked about it’s unusual that this case went to a jury trial

The 2025 Global Study on Closing the IT Security Gap

Ransomware, network and application attacks, insider threats and denial of service attacks are just a few of the threats putting organizations on high alert. The increasing sophistication of cyber criminals—as well as these cyber criminals adopting AI–makes it more important than ever to become aggressive in closing security gaps in the IT infrastructure.

 New approaches to closing the IT security gap are needed. In 2023, organizations had an average of five security breaches over a 12-month period. This increased to an average of six incidents in 2024. With the difficulty in reducing breaches and security incidents, organizations are changing their activities and use of technology. Since 2023 the most significant changes are the use of comprehensive penetration testing (an increase of 17 percent of respondents), implementation of a secure and continuous data protection and backup strategy (an increase of 17 percent of respondents) and prioritization of rapid attack and breach detection (an increase of 16 percent of respondents). For the first time, the study asked if network detection and response (NDR) (42 percent), kernel detection/ silicon root verification (39 percent) and micro segmentation (32 percent) are new technologies deployed to close the IT security gap.

Optimizing AI technologies to close the IT security gap

 AI’s ability to close the cybersecurity gap depends upon close collaboration between network and security teams. Thirty-nine percent of respondents say their organizations have adopted AI to close the IT security gap. In addition to improving collaboration between network and security teams (34 percent of respondents), other AI priorities include aiding in threat investigations (32 percent of respondents) and detecting changes to the organizations’ security posture (30 percent of respondents).

 To have a successful AI strategy, organizations need assurances about AI accuracy, privacy safeguards and data leakage prevention. Organizations considered uncertainties about AI accuracy, difficulties in ensuring data privacy and difficulties in preventing data leakage their greatest challenges with AI (all 44 percent of respondents). Another possible deterrent to closing the IT security gap is not having the confidence that their organizations know and are able to secure all AI assets including infrastructure, models and data. Only 43 percent of respondents say their organizations are very or highly confident they have that visibility.

 Organizations considering the use of AI for business purposes need to evaluate the possible complexity the technology will add to their operations. Fifty-three percent of the 39 percent of respondents who have adopted AI are using AI for business purposes. The security risks created when AI is used for business purposes are increased complexity because of the addition of new security tools (57 percent of respondents), potential theft or leakage of confidential and sensitive data (47 percent of respondents) and the inability to recover lost data in the event of an attack or disaster (44 percent of respondents).

 Why the IT security gap continues to put organizations at risk

 Not having the necessary skilled IT professionals continues to be the number one barrier to closing the IT security gap.  While fewer organizations are reporting shortages in security staffing, skills and experience (30 percent vs. 39 of respondents in 2023), shortages are still affecting organizations’ security posture. Additional barriers to closing the IT security gap include security solutions that can’t keep up with exponentially increasing amounts of data and difficulty in complying with IT security and privacy industry standards or regulations (each 29 percent of respondents).

 Too many vendors to manage and lack of collaboration between network and security teams can weaken organizations’ cybersecurity posture. Fifty-six percent of respondents say managing multiple security vendors is challenging and, as a result, can diminish their organization’s security posture. Forty-seven percent of respondents say it is difficult to achieve collaboration between network and security teams. Such collaboration is critical to preventing friction between IT and security teams that hinder efforts to put an effective strategy in place.

 New approaches to securing the modern workplace

 Secure Access Service Edge (SASE) frameworks combine networking and security capabilities into a unified, cloud-based solution, ensuring seamless access and protection for distributed workforces and enterprise assets.

Organizations are at various stages in their SASE deployment. In 2024, 23 percent of respondents say their organizations have deployed SASE, 23 percent of respondents say they will deploy in 12 months and 19 percent of respondents say their organizations will deploy SASE sometime in the future.

Reduction of costs, improved application performance and improved security posture are priorities for deploying SASE. Thirty-seven percent of respondents say their organizations deployed SASE first to reduce costs and improve application performance for users and branches. Thirty-six percent of respondents say their organizations started their SASE journey with an SSE deployment to improve security posture and increase protection. The number one SASE deployment strategy is to engage a best-in-class SD-WAN vendor that integrates with SSE vendors (30 percent of respondents) followed by engaging a best-in-class SSE vendor that integrates with SD-WAN vendors (27 percent of respondents).

Universal Zero Trust Network Access (ZTNA) is a security framework that allows organizations to grant secure access to applications for subjects regardless of their location. Forty-eight percent of respondents say their organizations have deployed universal ZTNA in some form. According to the research, the three most important characteristics of the universal ZTNA approach are enabling least privilege access to support zero trust (35 percent of respondents), ensuring a seamless access experience for users anywhere (30 percent of respondents) and securing IoT devices and users (29 percent of respondents).

Closing IT security gaps in hybrid cloud environments.

Organizations are securing their hybrid cloud environments in multiple ways. The processes prioritized to minimize the risk in a hybrid cloud environment are the implementation of a defined cybersecurity compliance framework (46 percent of respondents) in 2024, securely shifting workloads from on-premises to the cloud (44 percent of respondents) and the modernization of IT security processes (43 percent of respondents).

Organizations are improving their ability to avoid security exploits and data breaches and secure workloads moving between on-premises and public cloud environments. Organizations appear to be making progress on several security fronts: The percentage of respondents who say challenges associated with avoiding security exploits and data decreased from 51 percent of respondents in 2023 to 43 percent of respondents in 2024. Similarly, the challenge of securing workloads moving from the edge to the cloud decreased from 43 percent in 2023 to 36 percent of respondents in 2024. The primary technology challenge continues to be enabling the free flow of data securely (46 percent of respondents).

Organizations are having greater difficulty in their ability to ensure the privacy of customer information and enable the free flow of information in the hybrid cloud environment.

Since 2023, more respondents say ensuring customers’ privacy and enabling the free flow of information has made it more difficult to secure the hybrid cloud environment (37 percent and 32 percent of respondents, respectively).

Separating storage and compute means they can be consumed, scaled, and priced independently. This allows businesses to pay for what they use and nothing more. Organizations in this research say their current security approach to compute and storage will change. The biggest changes organizations indicate they will face in separating storage and compute will be moving their current security approach to the cloud (28 percent of respondents), managing a combination of solutions from security and hybrid cloud infrastructure providers (25 percent of respondents) and requiring vendors to supply new security solutions (24 percent of respondents).

More organizations are making server decisions based on the security inherent within the platform (62 percent of respondents, a significant increase from 48 percent in 2023). Fifty-eight percent of respondents say their organizations require servers that leverage security certificates to identify that the system has not been compromised during delivery. Fifty-eight percent of respondents say data protection and recovery are key components of their organizations’ security strategy and 58 percent of respondents say their organizations require infrastructures that leverage chip and/or certificates to determine if the system has been compromised during delivery.

Best practices of high-performing organizations

Twenty-one percent of respondents reported that their organizations are highly effective in keeping up with a constantly changing threat landscape and closing their organization’s IT security gap. We refer to these organizations as “high performers” and compare their responses to the non-high performer respondents, referred to as “other”.

Collaboration between network and security teams is essential to a successful security strategy. Fifty-four percent of high performers vs. 40 percent of others have achieved collaboration.

High performers are most likely to have a vendor consolidation strategy. Too many vendors to manage affect an organization’s security posture. Fifty-nine percent of high performers vs. 51 percent of other respondents have a vendor consolidation strategy to improve ROI.

High performers are more likely to adopt AI. There is a significant difference in high performers and others adoption of AI (61 percent of respondents vs. 49 percent).

High performers place a higher value on NAC solutions and the integration of NAC functionality. Respondents were asked to rate the importance of NAC solutions and integration on a scale of 1 = not important to 10 = highly important. The importance of NAC solutions (60 percent vs. 41 percent) and integration of NAC functionality (56 percent vs. 41 percent) are rated higher by high performers.

When it comes to universal zero trust network access, high performers place notably greater importance on seamless access experience for users anywhere. High performers are more positive about seamless access and consistent enforcement at every location (34 percent of high performers vs. 26 percent of other respondents). Twenty-nine percent of high performers vs. 22 percent of the others rate consistent enforcement at every location higher than the other respondents.

High performers are more likely to make the identification and authentication of IoT devices accessing their networks critical to their organizations’ security strategy. Fifty-nine percent of high performers vs. 48 percent of the others are more focused on identifying and authenticating IoT devices with access to their organizations’ security strategy.

High performers are more likely to require infrastructure that leverages chip and/or certificates to determine if the system has been compromised during delivery. Sixty-six percent of high performers v. 49 percent of the others require infrastructure that leverages chip and/or certificates to determine if the system has been compromised during delivery.

Recommendations to close the IT security gap

To close the IT security gap organizations are making significant changes in their strategies to minimize threats within the IT infrastructure. These include implementing NDRs, conducting comprehensive penetration testing, prioritizing rapid attack and breach detection and implementing a secure and continuous data protection and back up strategy. New in this year’s research is organizations’ adoption of AI (39 percent of respondents). Organizations primary goals for AI are to improve collaboration between network and security teams, to aid in threat investigations and to detect changes in the organizations’ security posture.

Following are actions to consider in the coming year.

  • Develop an AI strategy. An effective AI deployment is dependent upon removing uncertainties about AI’s accuracy, ensuring the privacy of sensitive and confidential data and assessing the risks to prevent data leakage.
  • Consolidate vendors to reduce redundancies of solutions that increase costs and create inefficiencies for the IT security team. To achieve consolidation of vendors evaluate spend categories to identify vendor overlap and map vendors’ capabilities to determine where cuts can be made.
  • Improve cyber resiliency by taking steps to reduce the time to recover from a critical system failure caused by a cyber incident. As shown in this research, only 35 percent of respondents say recovery can be achieved in less than one hour (12 percent) or in 1 to 4 hours (23 percent). This includes making sure technologies are used efficiently and having a cybersecurity incident response plan in place to navigate a security crisis.

Part 2. Key findings

Ponemon Institute surveyed 2,120 IT and IT security practitioners in the United States (635), the United Kingdom (291), Germany (371), France (197), Australia (180) and Japan (446) in 2024 for publication in 2025. In this report, we present the 2023 and 2024 global findings. The audited findings are presented in the Appendix of this report. We have organized the findings according to the following topics.

  • Barriers to closing the IT security gap
  • Closing the IT security gap with artificial intelligence
  • Imperatives for controlling access: zero trust, NAC, SASE and universal ZTNA
  • Securing the hybrid cloud
  • The separation of compute and storage
  • Country differences
  • Best practices in closing the IT cybersecurity gap

To read the rest of this report, visit Hewlett Packard’s website.

A decade of heartbreaks: His identity has been used in hundreds of romance scams

Bob Sullivan

I sat down at his table and he had probably 100 cards and letters and gifts and boxes and he said, ‘I bet there’s at least 500 …. This isn’t nearly all of it.’ And he really lost count. There were just stacks of love letters and gifts and cards, and it just… the emotional power of sitting at his kitchen table that was just covered in evidence from women who believed that they were in love with him. — ABC News reporter Lisa Fletcher

Cards. Flowers. Candy.  Gifts that just never stop. It might sound quaint at first, even charming.  But every one of these love stories ended the same.  With Pat Marsh pleading for the sender to stop. Sometimes, that conversation happens at his front door…with anger and even violence hovering in the air.

“These people have also come to my house….And this is where it gets dangerous,” he told me for a recent episode of The Perfect Scam, the podcast I host for AARP.

“After about 6 months of this, one night… There was a knock at my door…and I was looking at a guy  and he was like… ‘you told me to come over.’ and I was like, “Dude, get outta here.” And that’s when he grabbed the door and he opened the door and tried to come in…  and my exact words were, ‘You’re playing a dangerous game. You need to get out of here.’ .. I would have shot him, if he had come into my house, I have shot him.”

“These people” are romance scam victims.  And the parade of victims who call, write and visit Pat Marsh has been relentless for nearly a decade. Marsh is a test pilot, a generally fascinating man who caught the attention of criminals back in 2017. They thought he’d make perfect bait for would-be lovers on dating sites, and by all accounts, the criminals were right.

Marsh is the victim of a particularly cruel kind of identity theft. No one can really say how many women and men have been enchanted by the fake Pat Marsh and various variations.  But here’s a hint: One police detective investigating a Pat Marsh romance scam in Easley, South Carolina – a widow who’d had $600,000 stolen — used email records to find 60 more cases.

Marsh is really the victim of industrial-scale crime, says Detective Eric Gillespie.

“The fake Pat Marsh here is actually probably a dozen if not more people,” he told me. “You’ve got professional outfits in West Africa and Southeast Asia that you might have 100 people who are the same person more or less, for lack of a better phrase.”

Even if you don’t believe you could ever be the victim of an online scam — and I think you are foolish for that — you should care about the surge in digital crime.  Pat Marsh is collateral damage in the ongoing international scam wars we are all fighting.  You can be next. All of us can get wrapped up in a scam even if we never communicate with a criminal.  That’s why these stories matter so much.

After a decade’s worth of investigations, TV news stories, and late-night door knocks, Marsh has no idea when his headaches will end.  He really has no control over it. Instead, an entire system needs to be changed. Online dating sites need to police their membership much more aggressively.  Banks and new money systems need to get better at policing suspicious transactions. And we all need to be more sympathetic about the isolation and boredom that create fertile ground for crime.

I hope you’ll listen to this two-part episode about the man with 1,000 fake lovers. If podcasts aren’t your thing, you can find a transcript here.

The 2026 Global Study on Postquantum and Cryptographic Security Trends

The purpose of this research is to provide important information about trends in post quantum, cryptographic security, PKIs and HSMs. Ponemon Institute surveyed 4,149 IT and IT security practitioners who are familiar with the use of these technologies in their organizations.

The countries in this research are the United States (552 respondents), United Kingdom/Ireland (573 respondents), Canada (396 respondents), DACH (553 respondents), Indonesia (369 respondents) and Singapore (482 respondents).

The post quantum threat is coming quickly, but will organizations be prepared? Quantum computing is a rapidly emerging technology that harnesses the laws of quantum mechanics to solve problems too complex for classical computers. The quantum threat, sometimes referred to as “post quantum”, is the inevitability that within the decade it will be capable of breaking traditional public cryptography such as RSA and ECC.

Only 38 percent of respondents say their organizations are preparing for the post-quantum threat, a slight decrease from 41 percent in last year’s report. Of these respondents, 44 percent from 2024 and 2025 are building a post-quantum cryptography strategy.

Thirty-two percent of respondents say their organizations are taking an inventory of their cryptographic assets and/or ensuring they are crypto agile. This is a decline from 38 percent of respondents in last year’s report. Testing within organizations’ systems and applications increased significantly from 10 percent of respondents to 21 percent.

The following summarizes the most significant research trends in postquantum and cryptographic trends

Organizations believe the PQ threat is imminent. Seventy-five percent of respondents agree and say a quantum computer will be capable of breaking traditional public key cryptography within 5 years (51 percent) or in 5 to 10 years (24 percent). Only 12 percent say it will never happen.

 The biggest challenge to reducing the quantum-threat and migration to post quantum cryptography (PQC) continues to be the inability to improve the discovery/inventory of their organizations’ cryptographic assets. Forty-one percent of respondents in this year’s study vs. 43 percent of respondents in last year’s study say the inability to improve visibility into their cryptographic assets is the greatest concern. Two concerns that have increased significantly are the lack of an adequate budget (39 percent in this year’s study vs. only 31 percent in last year’s study) and lack of in-house expertise (38 percent in this year’s study vs. only 28 percent in last year’s study).

Fifty percent of respondents say a successful quantum attack would have a serious impact on their organizations and industries. Fifty percent rate the potential impact as serious, but only 36 percent of respondents rate the adequacy of government policy and public-private coordination on quantum readiness as more than adequate. A successful quantum attack against organizations and industries could result in the loss of access to encrypted critical infrastructure (58 percent of respondents) and exposure of long-term sensitive data such as health records and trade secrets (59 percent of respondents).

The lack of visibility into the cryptographic estate, certificates and keys and secrets puts organizations’ cryptographic security at risk.  Only 43 percent of respondents say their organizations have full or complete visibility into their organizations’ cryptographic estate and only 43 percent of respondents say they have full or complete visibility into certificates across the organization and only 40 percent say they have full or complete visibility into keys and secrets across the organization.

Private cloud-based applications and mobile device authentication applications that use PKI credentials declined significantly from 2024. Private cloud-based applications using PKI declined the most (56 percent of respondents in 2024 vs. 32 percent of respondents this year). Mobile device authentication decreased from 60 percent of respondents to 41 percent of respondents). The top applications using PKI credentials are private networks (52 percent of respondents), SSL certificates for public facing websites and services (50 percent of respondents) and document/message signing (45 percent of respondents).

Internal corporate certificate authorities (CAs) are most often used to deploy PKIs but have declined since last year. Forty-six percent of respondents in this year’s report use CAs to deploy PKI and 60 percent of respondents in last year’s study. Business partner provided service increased the most from 18 percent of respondents in last year’s report to 40 percent of respondents in this year’s study. Private CAs running within a public cloud increased from 21 percent of respondents last year to 37 percent of respondents this year.

The most important security certification when deploying PKI infrastructure is Common Criteria EAL Level 4+ (54 percent in this year’s study vs. 57 percent of respondents in last year’s study). The second most important certification is FIPS 140-2 Level 3. However, its importance has declined significantly from 55 percent of respondents to 32 percent of respondents.

The biggest uncertainty and concern about the evolution of PKI are PKI technologies and external mandates and standards. When asked what the greatest areas of change and uncertainty to PKI will be, 49 percent of respondents say it is PKI technologies, an increase from 43 percent in 2024 and external mandates and standards, an increase from 37 percent of respondents in 2024. Budget and resources, increased significantly to 43 percent of respondents vs. 30 percent of respondents.

More organizations use HSMs and use HSMs to secure PKI. Sixty-six percent of respondents in this year’s research vs. 55 percent of respondents in last year’s research say their organizations use HSMs. Sixty-three percent of respondents in this year’s research vs. 51 percent of respondents in last year’s research say their organizations use HSMs to secure PKI.

The top areas of deployment to secure PKI are online roots and offline roots. According to last year’s research, 47 percent said they are deployed to secure PKI in online roots and 42 percent said they are deployed to secure PKI in offline roots.  

Part 2. Key findings

 In this section we present the research results in detail. The compete audited findings are shown in the Appendix. The report is organized according to the following topics. Whenever possible, trends in research findings from last year’s Entrust study are included. 

  • Postquantum: The Threat and the Readiness Journey
  • Cryptographic Security and Management
  • Trends in PKI Security and HSMs

To read key findings and the rest of this report, visit Entrust’s website here. 

As AI enteres the real world, it’s going to crash into the Plateau Effect

Bob Sullivan

We just learned that Waymo is recalling about 4,000 self-driving cars because they can’t read highway construction signs.

According to Road & Track, some Waymo cars “failed to recognize and drove past ramp closure signs into pre-planned freeway construction zones; Waymo recorded six of these events in April 2026 in Phoenix, Arizona. In an additional seven incidents in May 2026 in San Francisco, California, the offending Waymos drove between cones designating lane closure.”

That’s a) terrifying b) a ridiculous engineering failure.  Construction is hardly a rare condition of highway driving. How did cars not equipped for this get released into the world?

Because someone, somewhere, believes certain sacrifices must be made for progress.

Waymo’s mistake is a very bad example of the kind of real-world exception conditions that have been derailing self-driving cars for more than a decade. Those same pesky, weird realities will soon make many wild promises about artificial intelligence look a equally silly — and cost a lot of investors a lot of money.

A few years ago, I wrote a book called The Plateau Effect with Hugh Thompson, former CEO of Symantec (this piece is my opinion alone, fyi).  The concept of the book is simple: plateaus appear everywhere in life, and they bedevil everything and everyone that seems to be making quick progress. People losing weight hit plateaus; people learning guitar or a new language hit plateaus; drugs hit plateaus. Once you start to look, you see plateaus everywhere. A simple example for geeks: Finding the first 99% of bugs in software is relatively easy. Finding the last few is often a nightmare — finding the last 1 percent can take longer than finding the first 99 percent. Sometimes, they’re never found. And so it will be for AI.  The Plateau Effect looks like one of those calculus curves where you approach…but never reach…a limit.

The Plateau Effect in Learning. Anything. (phuongvu.me)

Life is full of these kinds of exception conditions.  Shit happens. One might say Murphy’s Law suggests that weird stuff like this is normal. Computers don’t do well with irregular inputs, as I’m sure you know. “That….does….not….compute…”


This is part 2 of a three-part miniseries on Artificial Intelligence.
Read part 1: Disarm AI, yes, but the Pope was just getting started
Read part 2: Artificial Intelligence needs a police blotter. Wait, it already has one!


Were a tech mogul sitting here, he’d furiously grab my keyboard at this point and tell me that millions of miles of data will solve this problem — there are only so many exception conditions on the roads, and eventually the supercomputer in the sky will be prepared to deal with all of them.  Even without The Plateau Effect, this feels foolishly optimistic to me. Exhibit A is Waymo’s current inability to deal with road construction.  But assuming that can be fixed, there will be weird, pesky, unexpected road conditions for as long as humans roam the Earth.  Dealing with the first 99% won’t be so hard.  Dealing with that last 1 percent will be very, very hard.  It’s not going to happen soon, with self-driving cars and many AI applications.

Elon Musk has been promising full self driving cars will be ready in a year or two since…2013.  There’s nothing new about this kind of hype cycle.  It’s meant to generate excitement and investment so early investors can make off with a lot of cash, funded by later investments.  And this pattern keeps working as long as investors believe in tomorrow.  Forget autonomous cars; the real future is on Mars!  And so it goes.

See, it’s easy to make a car that can ride on highways which can follow predictable patterns — roads you could drive with your eyes closed.  But when an 18-wheeler loses a tire tread and cars in front of you start to swerve and dart, well, your eyes better be open.  Another example, shared with me recently by Sean McGregor of the AI Incident database: When a dog gets loose in stop-and-go traffic, What Would Waymo Do?

But what about all the dire warnings of AI software teaching itself how to destroy humanity? First off, if you were actively building a tool that would blow up the world, wouldn’t someone at these firms throw the assembly line emergency stop switch? But more to my point here: I suspect AI investors don’t mind all these doomsday scenarios because they help build buzz. I’ve watched entire documentaries about scary AI futures that don’t even raise the question: Are we sure this stuff will actually work? The a priori assumption that we’re successfully building God is pretty valuable to these early investors.

I’m *NOT* saying none of this stuff works.  AI is great at writing perfectly trite emails, though my smartphone recently replied “how are you?” to someone on my behalf when I had no intention of asking.  That was awkward.  Can a Tesla in FSD mode drive better than a teenager playing with his smartphone? Yes, I think so. I drive a car with a lot of automated safety technology that I think works great.  But can a Tesla on autopilot deal with a dog on the highway better than a human with good judgment? Not yet. And, I’ll wager, not for a long time.

I’m harping on this point because ignorance of The Plateau Effect sets up a perfect situation for those who benefit from AI hype.   Tech moguls and PR firms generate a lot of attention and money with wild promises about tomorrow. At trade shows, I used to call this the ‘next quarter’ game.  People would hawk all kinds of great new hardware and software through amazing demos in Q3, then promise it would be ready by Q4. But in tech, Little Orphan Annie is a liar. Tomorrow is much more than a day away.

I don’t care so much about people who want to play this game with investment cash. That’s their business. What I care about is the “sacrifices” that tech firms will decide are acceptable as they run harder and harder into the Plateau Effect.  Regulators and voters have to be ready to recognize the dangers we are about to encounter, and the language that will used to distract us. Like Google itself, AI will be in beta mode for a long time.

The State of Cybersecurity Marketing Influence 2026 From awareness to selection: How buyers evaluate vendors

Enterprise cybersecurity buyers are raising the bar for technical depth, proof, and measurable outcomes. Marketers need clarity on what has changed, what still drives influence, and which approaches require reevaluation or retirement.

To address these questions, NOLA Marketing and the Ponemon Institute partnered to conduct an in-depth study of enterprise security leaders. The study reflects input from 320 enterprise cybersecurity decision-makers across mid- to large-enterprise organizations, each directly involved in cybersecurity purchases and renewals.

The research examines how CISOs and security leaders engage with marketing content, how AI is impacting the buying process, and which assets and approaches materially influence vendor evaluation and renewal. This report provides marketers with clear, data-backed insights into what resonates with today’s security leaders, and what no longer does.

Encouragingly, a majority of respondents agree that cybersecurity marketers provide information that informs purchasing decisions. Buyers continue to engage with content that marketers produce while signaling strong demand for more technically substantive assets, particularly solution briefs, website content, white papers, research reports, webinars, and technical workshops.

At the same time, the responses show areas for improvement. More than half of respondents cite gaps in marketing content, including insufficient technical and operational detail, a lack of evidence-backed claims, limited transparency about tradeoffs, and an unclear articulation of how solutions integrate with existing security stacks. Buyers indicate a need for stronger evidence-based positioning, clearer articulation of real-world performance, and tighter alignment to measurable business and risk outcomes.

The buyer journey is evolving. More than a third of respondents report using AI in the product selection process, leveraging AI overviews, chatbots, product comparisons, and even RFP drafting to accelerate research. However, trust in AI-generated outputs remains mixed, and receptiveness to on-site AI chatbots is divided, suggesting that while AI-assisted discovery is expanding, credibility and substantive content remain decisive in vendor selection.

This report presents detailed survey findings on where marketing resonates, where credibility gaps persist as buyer expectations shift, and how AI is reshaping evaluation behavior. The following analysis translates these findings into clear strategic implications for marketing strategy, content development, and go-to-market execution.

Key findings

Credibility stands out as the primary gap. Although 58% agree marketing supports decision-making, 52% say messaging lacks technical depth, and 49% cite insufficient ROI justification.

Peer-driven influence leads vendor discovery. Peer recommendations rank highest at 55%, outpacing analysts, consultants, and traditional marketing channels.

Research-backed content drives selection. Research and survey reports have the strongest direct impact at 46%, exceeding that of all other asset types.

Buyers demand deeper digital evaluation assets. Website content leads demand at 45%, followed by solution briefs at 41%, signaling that buyers rely heavily on core digital and product-centric assets during evaluation.

AI is embedded into vendor research workflows. More than one-third of security leaders now use AI overviews and chatbots, with 51% using chatbots for product research and 48% using AI overviews

Impressions of cybersecurity marketing effectiveness

A majority of respondents (58%) agree that cybersecurity marketers provide the information needed to support informed purchasing decisions, with 25% strongly agreeing. This data indicates that marketing content contributes meaningfully to buyer evaluation processes.

However, 42% of respondents are either unsure or disagree. While marketing is widely regarded as beneficial, strong endorsement is not universal. The higher proportion of general agreement compared to strong agreement suggests moderate endorsement of marketing’s ability to support the purchase decision process.

In enterprise security environments, where purchases involve technical scrutiny and risk accountability, partial confidence can limit influence. Marketing meets baseline informational needs but does not consistently deliver the depth, evidence, or clarity required to fully satisfy buyer expectations.

When asked to identify the primary problems with marketing content, respondents consistently cited gaps in credibility and specificity.

Dissatisfaction centers on credibility, validation, and contextual clarity. The friction points align closely with areas that influence later-stage evaluation and justification, rather than early-stage discovery. Nearly one in two buyers report missing proof, unclear ROI, or difficulty understanding stack integration. Marketing reaches buyers and can be effective, but it often lacks the operational depth required to sustain confidence.

To read the full report, visit Nola Marketing’s website by clicking here. 

Artificial Intelligence needs a police blotter. Wait, it already has one!

Click to visit the AI incidents database

Bob Sullivan

In our world of black and white, it’s difficult to be a tech skeptic without being labeled a Luddite.  The Holy Grail is progress, so the thinking goes, and any pesky question asking threatens to stifle innovation.  Do you want us to lose to the Chinese!?!?

It’s ok, I’ve been doing this a long time.  Not so long ago, my nickname among CNBC bookers was “Big Data Hater.”  You remember the age of Big Data, don’t you?  If you don’t, it was yet another marketing moniker that took over the tech world for a few years, stoking stock valuations everywhere it went. A mini dot-com boom, if you will.  Big Data, unfortunately, often became synonymous with Bad Data, which always gives bad results, no matter how much data you shove into the GIGO machine. Today, we call these Large Language Models, which sound much more sophisticated, but suffer equally from the same garbage problem.


This is part 2 of a three-part miniseries on Artificial Intelligence.
Read part 1: Disarm AI, yes, but the Pope was just getting started 


Back then, I would protest with a glint in my eye — how can someone hate data? That’s like hating atoms! Some of my best friends are data!

I don’t hate data. Or tech.  What I hate is thoughtless “progress” without discernment about side effects and collateral damage. And I really hate when the progress … is promised, down the road — soon! — while the roadkill piles up today.  What’s the roadkill of this never-ending tech bubble cycle? Pension funds that are crushed when the bubble bursts. Workers who are laid off in the name of cost savings needed to offset investments.  Kids who end up with addiction machines in their pockets because there’s no other legitimate business model for social media. Adults who’ve sacrificed every shred of human privacy so they can be stalked by ads for items they purchased last week. And so on.

Yes, the consequences are real, and they are here — even if the innovations are…just around the corner.

I’m not arguing that AI isn’t real. Already, it’s freed an entire generation from writing trite, jibberish-laden emails back and forth at work.  AI can turn meetings that should have been an email into a summary of said email.  That could be real progress — but let me know when those meetings are actually canceled.

Can AI do a great job of writing a meeting summary for people who weren’t really paying attention anyway? Yes, absolutely. Can it pull out that one critical moment in the meeting which most attendees missed…which might very well be what was left unsaid?  Ha! (You’ll read about this in part three of this miniseries)

AI is great at writing code, getting rid of some of the grunt work of the digital age.  It helps people with blank page syndrome get a start on papers and presentations.  And it’ll do a fine job of summarizing large amounts of material for people in a hurry. A great application I read about recently involved practicing physicians who have scant time to read all the latest medical research. It can do these things today.

As for tomorrow — there seems good reason to believe AI will be great at finding needles in research haystacks, which could very well lead to amazing medical advances.  I will be the first to cheer on this work. I’m sure I’ll need it someday.

But tech titans have a decades-long pattern of racing forward with innovations, intermediate consequences be damned. Of doing things simply because we can, not because we should — in fact, not even asking if we should.  And, specific to my main work right now, of creating tools that are easy to abuse and darn near impossible to stop.

I am not a Luddite. I think tech does more good than bad. But I think in a playoff series, “good” wins in the 7th game, and probably in overtime.  It’s often a close call.  We can’t ignore the bad things that AI will do because it might slow progress a smidge. The best thing we can do is air every single one of these side effects and work to eliminate them. That’s how penetration testing has always been done. That’s the ethos of open source software. More than ever, we need to approach the coming age of AI that way.

That’s why I was so happy to learn recently about the Artificial Intelligence Incidents Database. It is what it sounds like — a list of mishaps caused by, or enabled by, AI.  I recently interviewed one of its leaders, Harvard fellow  Sean McGregor, for The Perfect Scam, a podcast I host for AARP.  McGregor is the kind of plain-speaking genius we desperately need right now.  We talked for an episode about a family who was targeted by an AI-generated photo of the family dog depicting him on an operating table, riddled with injuries from a car accident. (That was incident 1,478 in the incident database). Naturally, our conversation covered far more.

McGregor made this point: Early on, the database was full of (funny?) incidents about AI failing to work properly. But increasingly, the database is loading up on tales of fraud committed by criminals using AI.  That might be the bigger problem, he suggests — the so-called dual use problem — as AI gets better at what it does, it gets better for the bad guys.  I left our chat thinking my sarcasm about AI’s clumsy failures might very well be misplaced.

Whatever you do, don’t call someone a Luddite because they’re worried about the future. We do get to decide what kind of future we want; we don’t have to just accept what Elon Musk gives us. In fact, I’d argue, that’s a poor choice.

Tristan Harris from the Center for Humane Technology appeared on CNN this week and made a very sharp point about incentives.  In the end, AI is going to become whatever the incentives nudge it to become. Right now, the only incentive on the table is shareholder value. That means AI will principally be used to eliminate labor costs.  The End.  But we have the chance to design other incentives right now. To reduce human suffering. To build more housing.  To make mass transit far more efficient. Heck, to enable human happiness.  Whoever told you that our society’s only goal is profit sold you a very shallow future. We can, we must, do better. An honest, real-time look at AI’s failings is going to be a big part of that.